Antivirus development
Detection engines, endpoint agents and the infrastructure behind them.
We develop antivirus and endpoint protection technology: scanning engines, behaviour monitors, update channels and management consoles. We work as an engineering partner for companies that ship security products or need detection built into their own software.
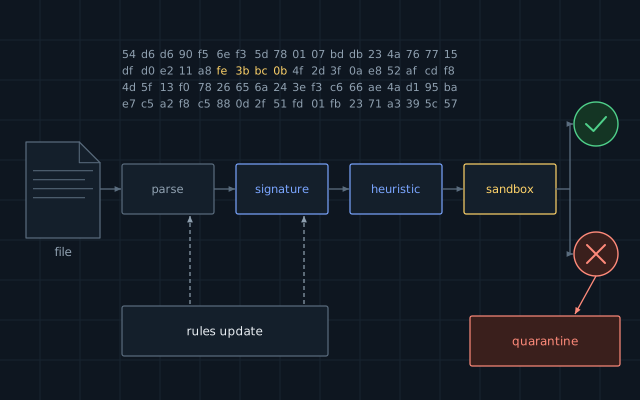
What we build
Scanning engines
Signature and heuristic scanners, archive and installer unpacking, file-format parsers hardened against malformed input.
Behaviour monitoring
Process, file, registry and network activity collected by kernel and user-mode components and matched against behaviour rules.
Detection rules and pipelines
YARA and custom rule sets, automated testing against collections of clean files, staged release.
Sandbox analysis
Isolated execution of suspicious files, with reports on what they actually did.
Management consoles
Central policy, quarantine, incident timeline and reporting for administrators.
Update infrastructure
Signed, incremental updates of signatures and engine, with a fast path for urgent fixes and a way back.
What you receive
- Engine or agent with documented interfaces
- Regression suite for detections and false positives
- Performance report on reference machines
- Signed update channel
- Operating procedures for analysts
Questions people ask
Do you sell a ready-made antivirus?
No. We build detection technology under contract, for companies that put it into their own products or infrastructure.
How do you handle malicious samples?
In isolated laboratories with no connection to client or corporate networks. We do not create or distribute malicious code.
How are false positives controlled?
Every rule is tested against a collection of clean files before release and rolled out in stages, so a bad rule can be withdrawn before it reaches most users.
Tell us what you need to build or protect
The first call takes forty minutes and commits you to nothing.