Security audits
An independent look at how your software can be attacked.
We review code, architecture and infrastructure, and carry out penetration tests on systems you own or are authorised to test. The result is a report developers can act on, not a scanner printout.
What we build
Source code review
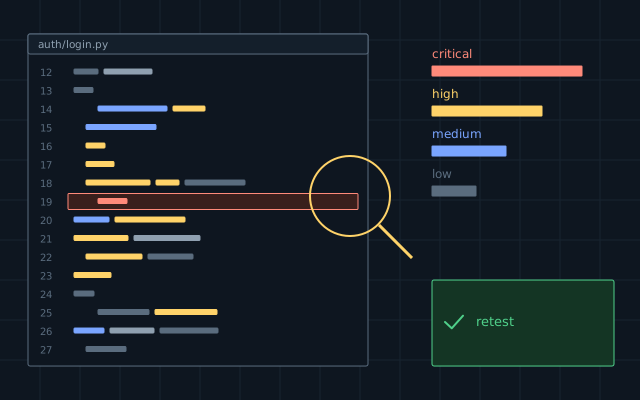
Manual review of authentication, authorisation, input handling and cryptography, supported by static analysis.
Web and API penetration testing
Testing against the common attack classes, with reproduction steps for every finding.
Mobile application testing
Local storage, transport, resistance to reverse engineering, and the server behind the application.
Infrastructure review
Servers, cloud accounts, access rights, network exposure and handling of secrets.
Dependency audit
Third-party components, known vulnerabilities, licences and integrity of the build.
Retest and remediation
We help fix the findings, then confirm that they are closed.
What you receive
- Findings ranked by real-world risk
- Reproduction steps for each finding
- Remediation advice for developers
- Summary for management
- Retest report
Questions people ask
What do you need from us to start?
A written authorisation that defines the systems and the period, a test environment where possible, and a contact for emergencies. We test nothing without it.
Will the test disturb production?
We agree the windows and methods in advance and avoid destructive tests on live systems.
Tell us what you need to build or protect
The first call takes forty minutes and commits you to nothing.